Software is being written faster than it can be secured, and AI has widened the gap. AI assistants are producing code at volume, agents are reaching into repositories and pipelines, and the supply chain underneath keeps getting attacked where teams have the least visibility.
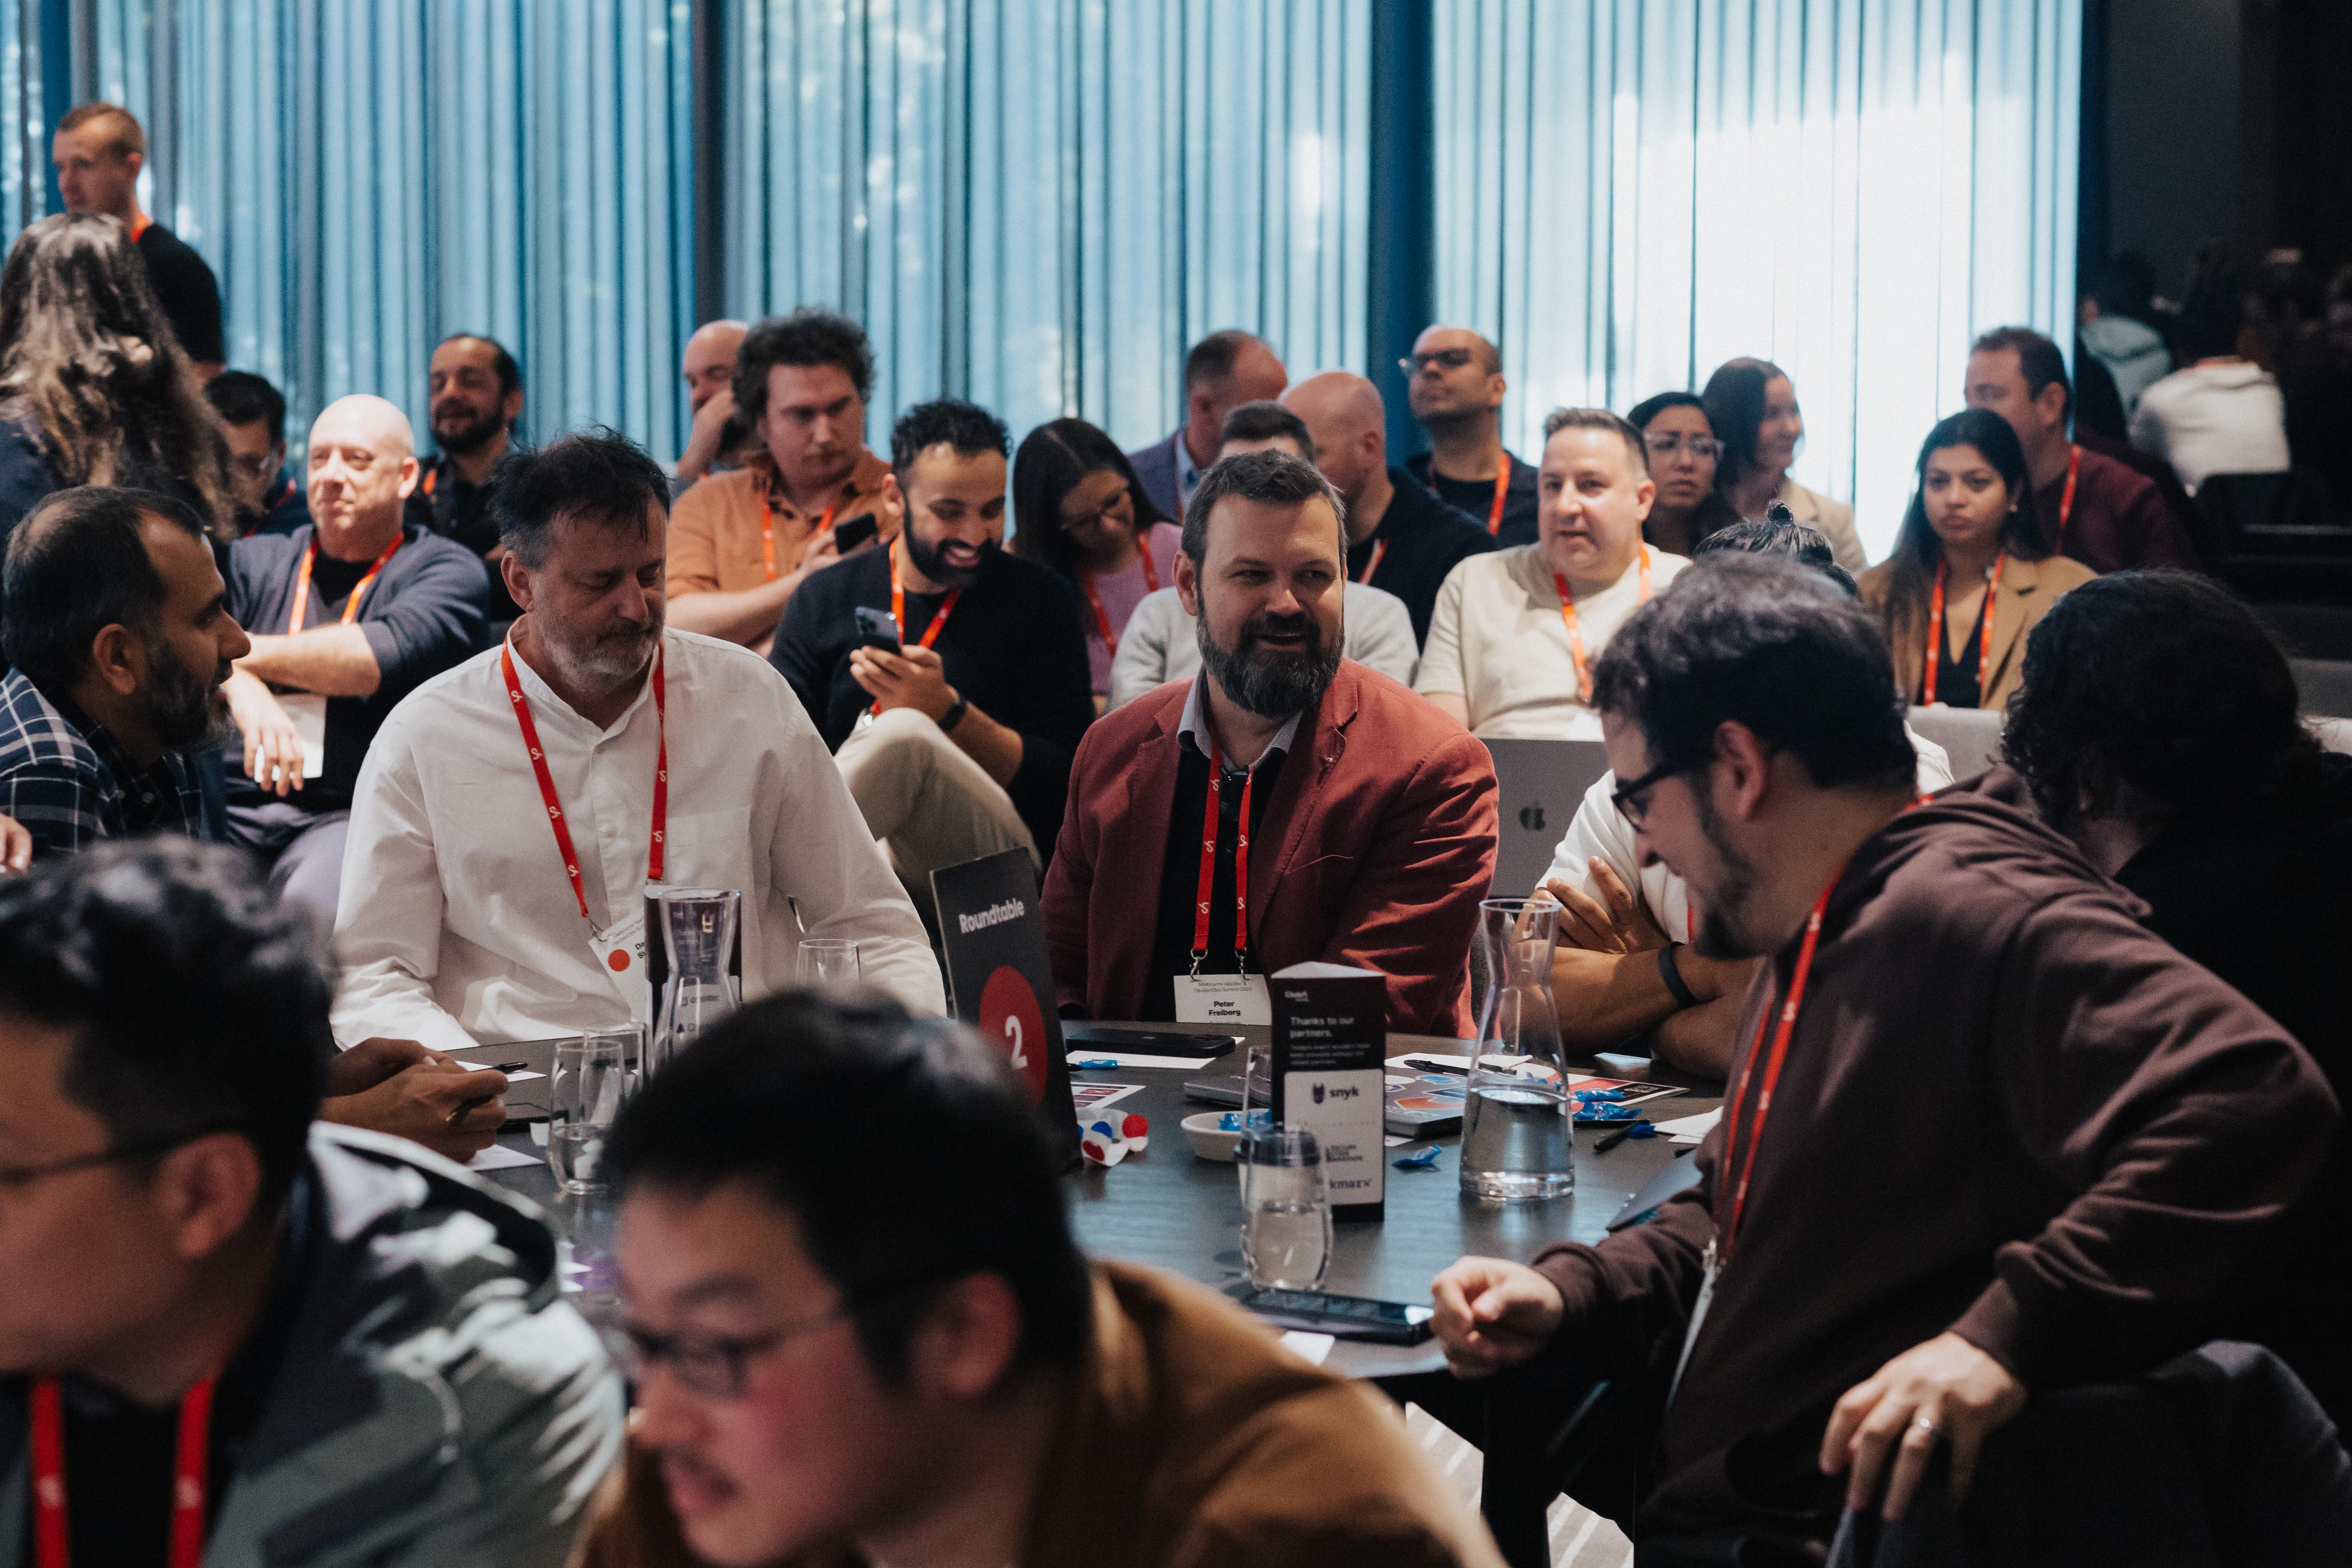
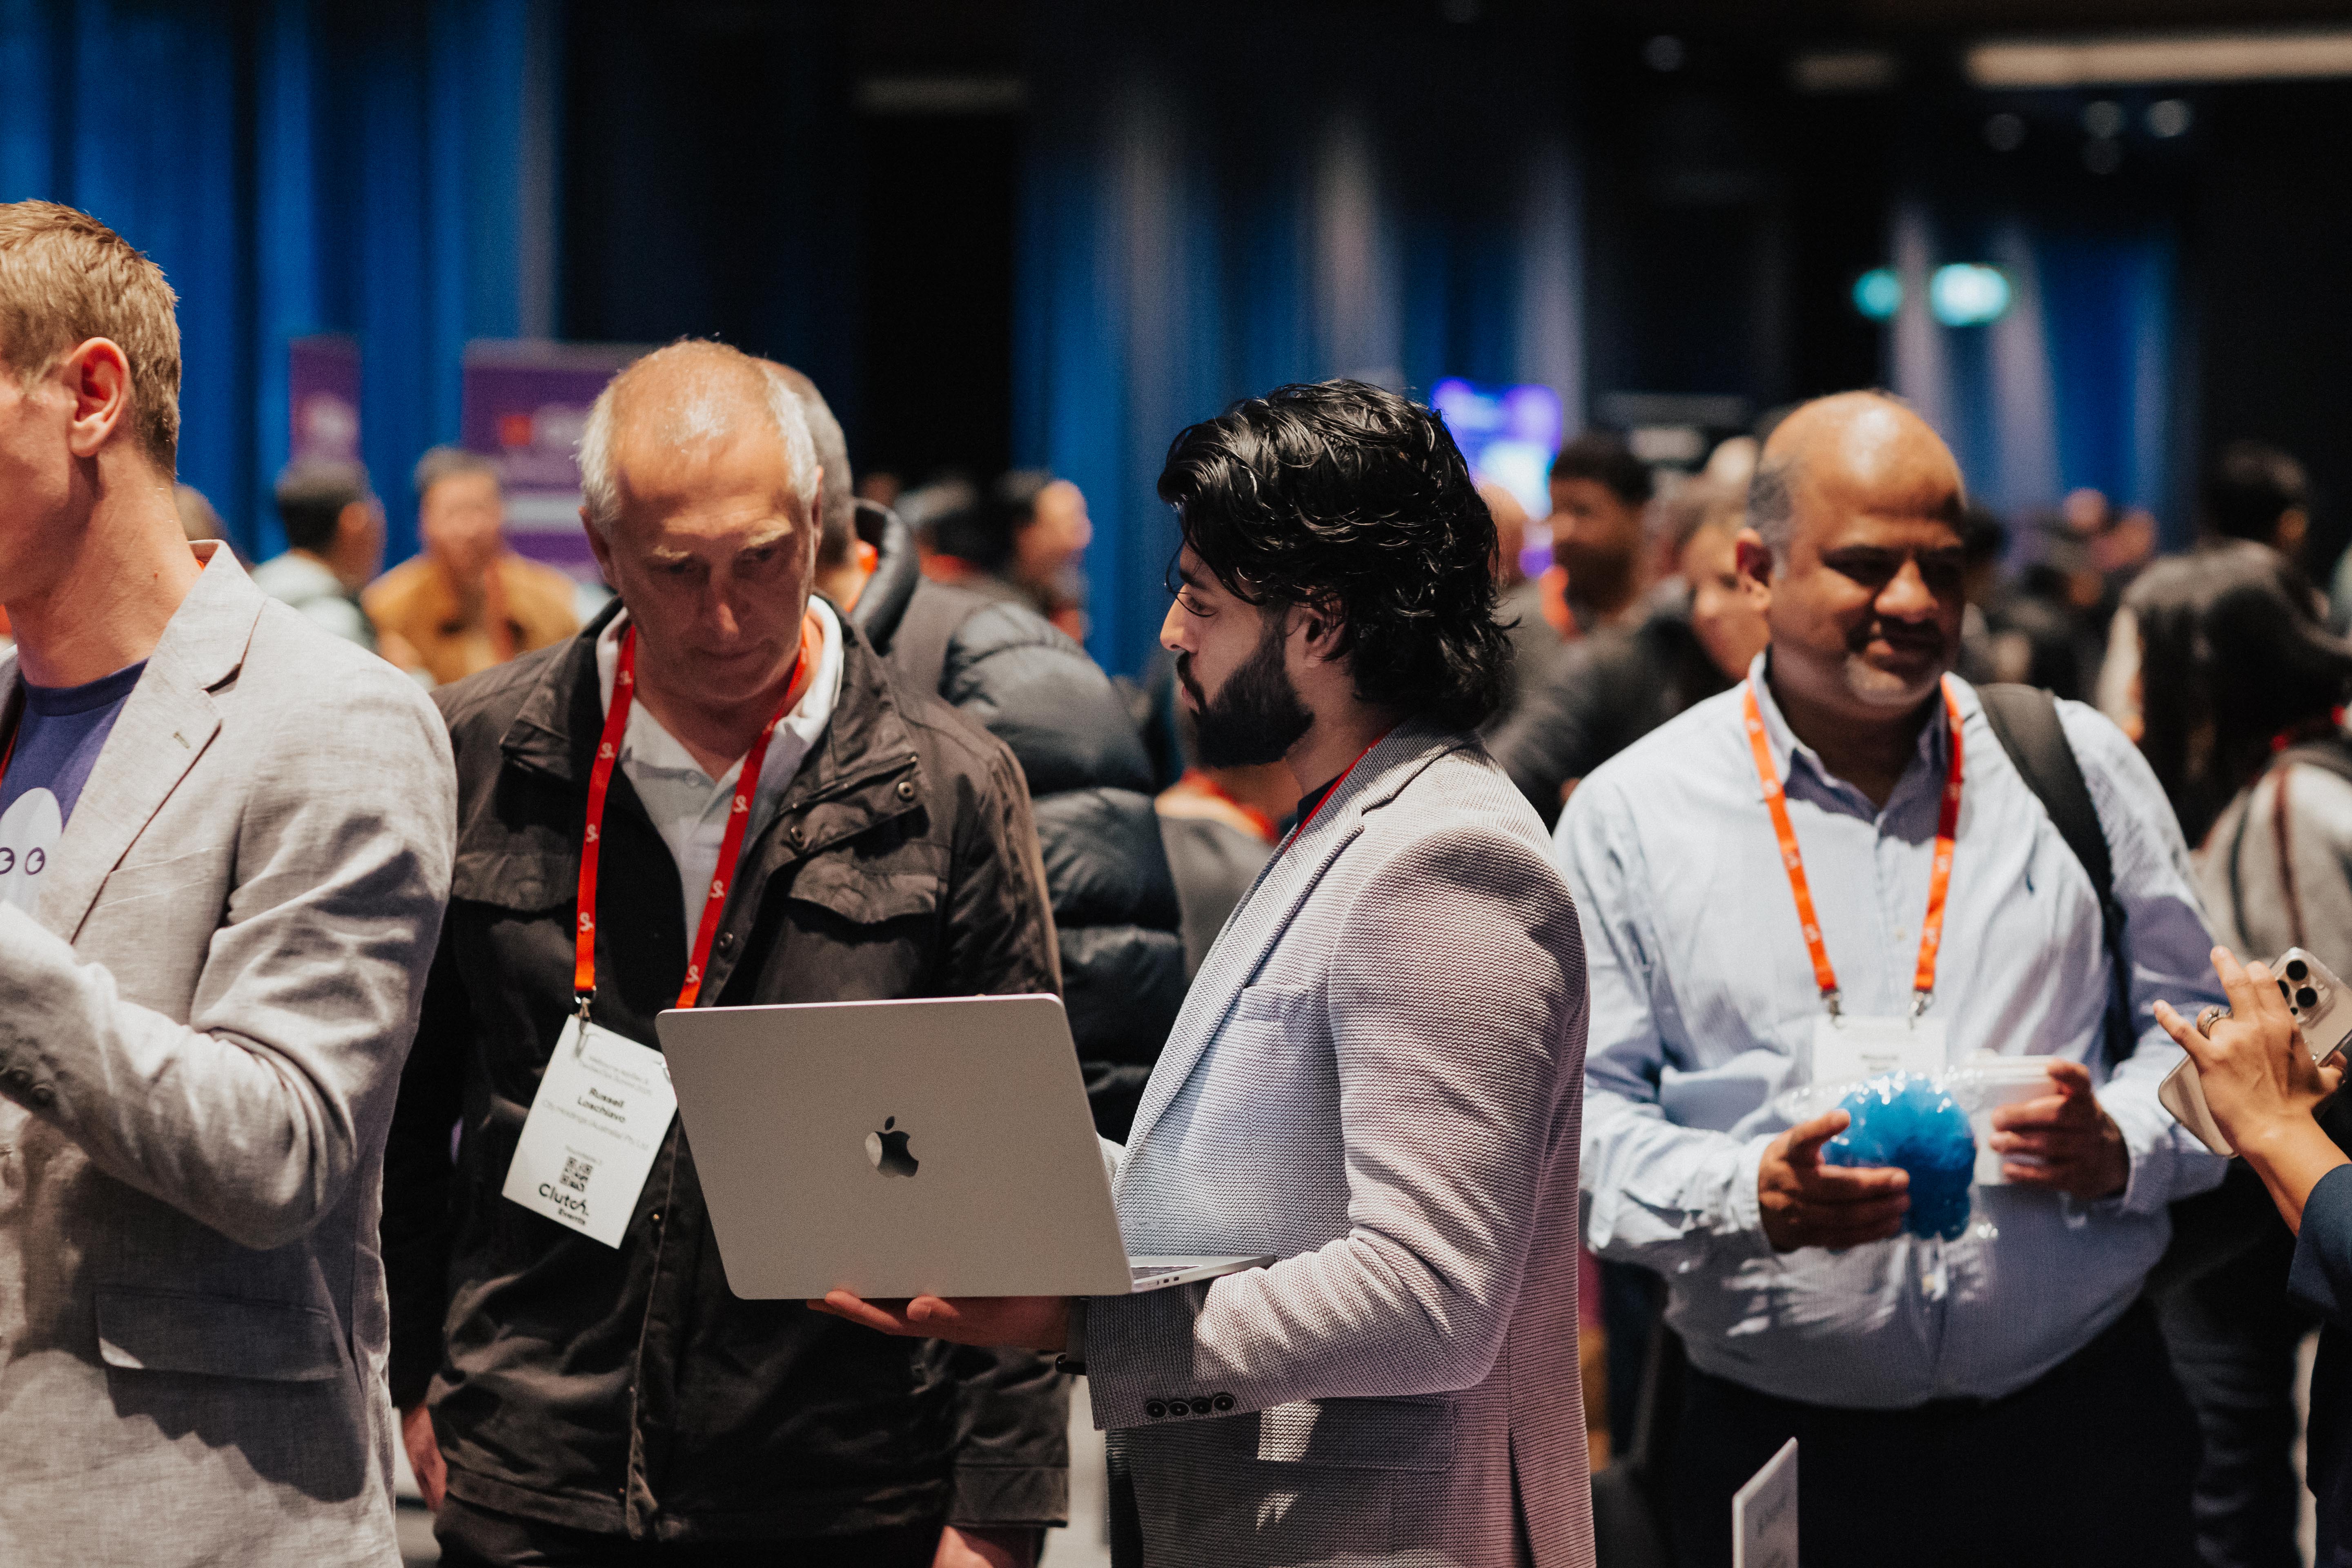
AppSec World is where the people responsible for that problem compare notes. Built on the AppSec summits that have hosted 519 practitioners from 325 organizations, it is a room of engineers, architects and security leaders rather than an audience of vendors.
The East Coast edition runs at the New York Marriott Marquis on September 9, with 150+ practitioners from across North America.
At most security conferences, application security is a stream inside a much broader event, never the room itself.
AppSec World is that room: the executives, programme owners and engineers who own how enterprise software gets built and shipped, comparing notes with their peers.
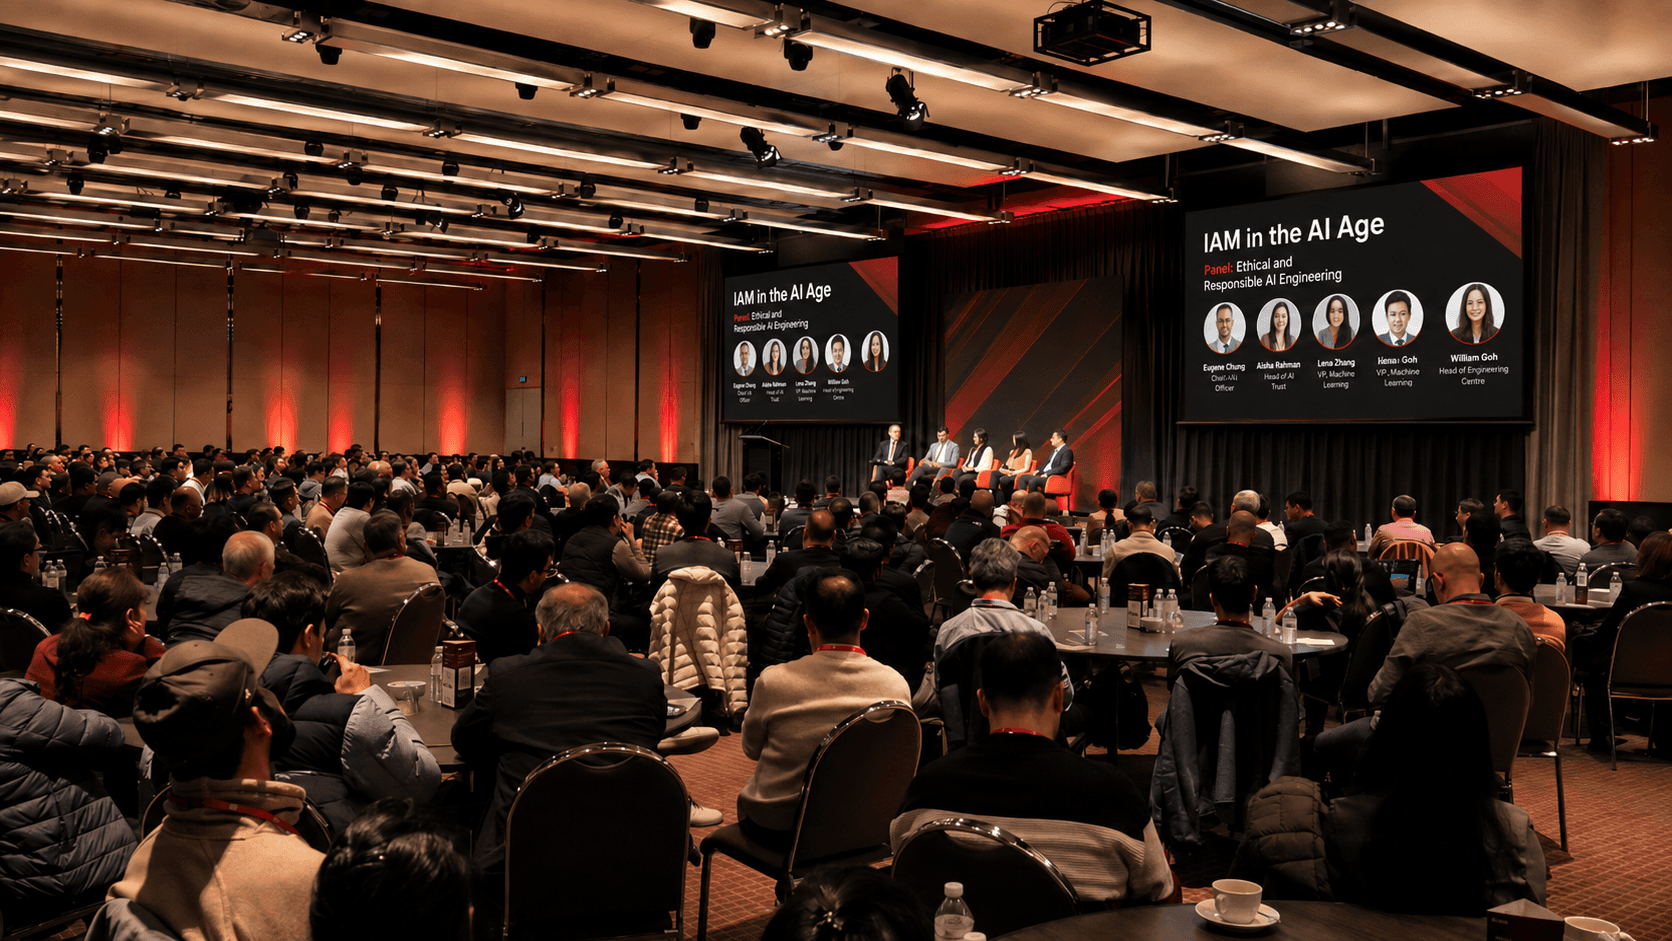
CISOs, CTOs and VPs of Security and Engineering who set the strategy and approve investment.
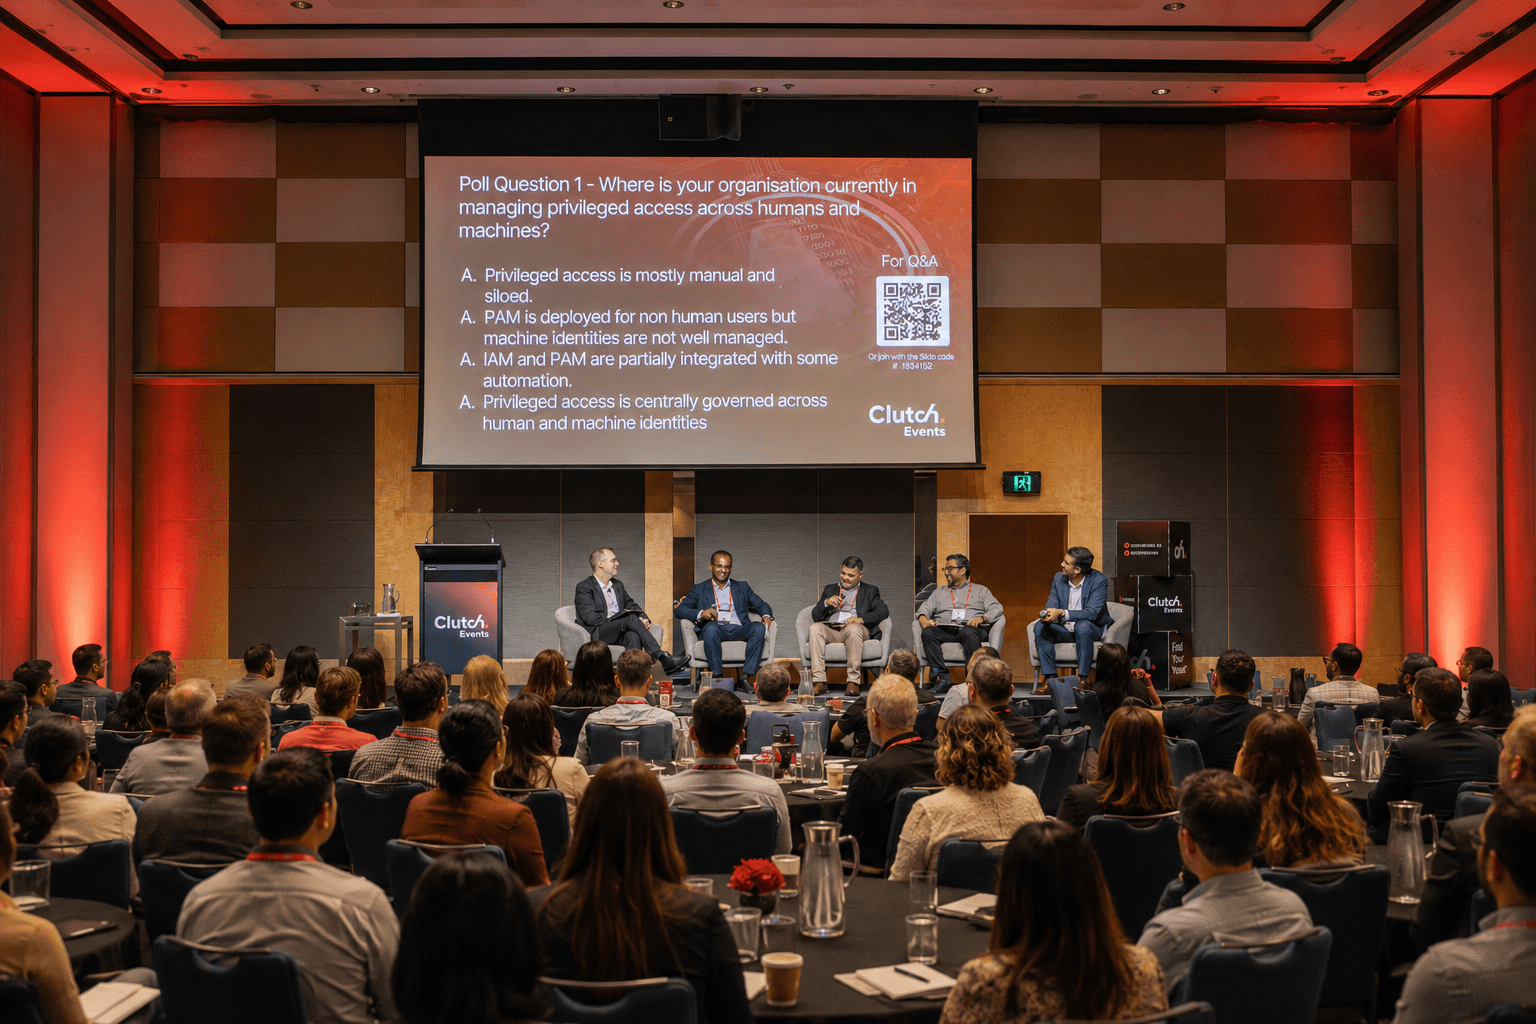
Heads, directors and managers of AppSec, Product Security and DevSecOps who own the roadmap and evaluate platforms.
The AppSec, product security, DevSecOps, platform and software engineers who build and operate the controls every day.
At least 85% of the audience are engineers, architects and security practitioners: the people writing the code, running the programme and dealing with the same problems you are.
Confirmed so far for East Coast AppSec World on September 9, 2027. More speakers will be announced as the program is finalized.

Agenda drops, speaker announcements and registration windows for East Coast AppSec World.