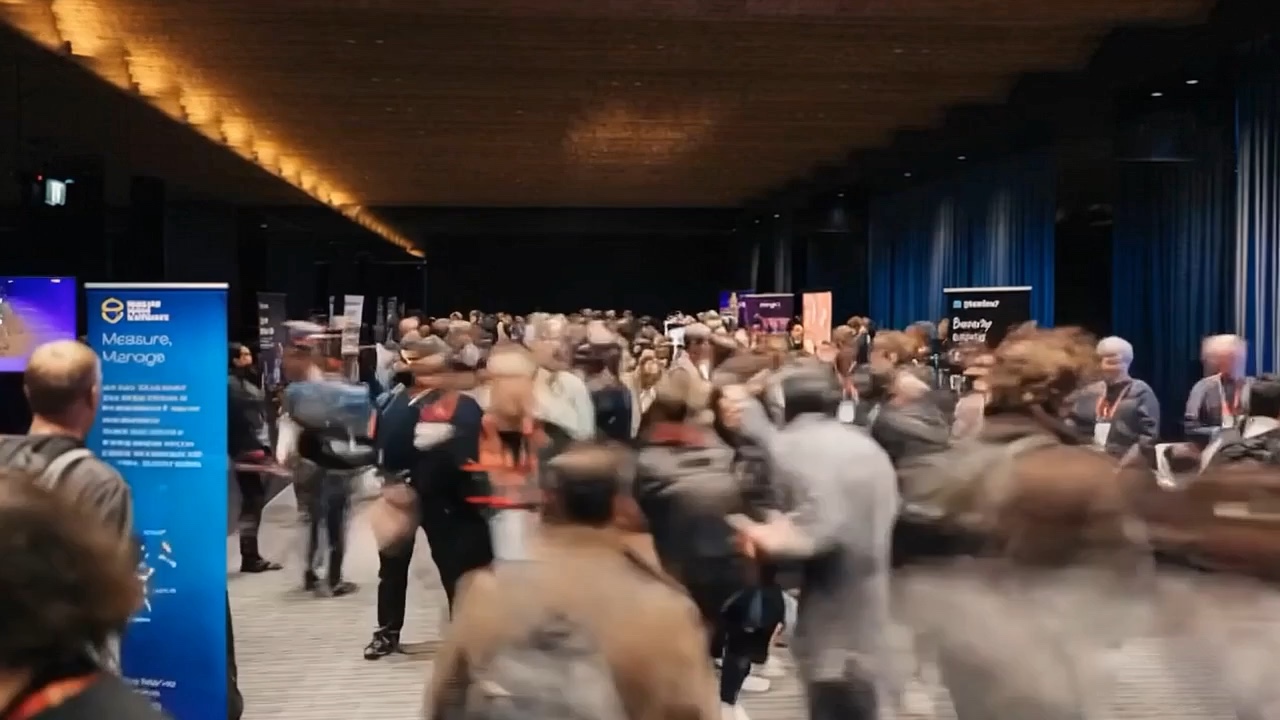
Since 2023, AppSec World has become the defining meeting place for the people securing how enterprise software gets built.
Trusted by more than 2,500+ AppSec & Engineering leaders worldwide the past 3 years, alongside the platforms, engineers and innovators deciding how software gets secured.
Software is being written faster than it can be secured, and AI has widened the gap: assistants are producing code at volume, agents are reaching into repositories and pipelines, and the supply chain underneath keeps getting attacked.
AppSec World is where the industry comes together to set the agenda, meet the people who matter and see what's coming next.
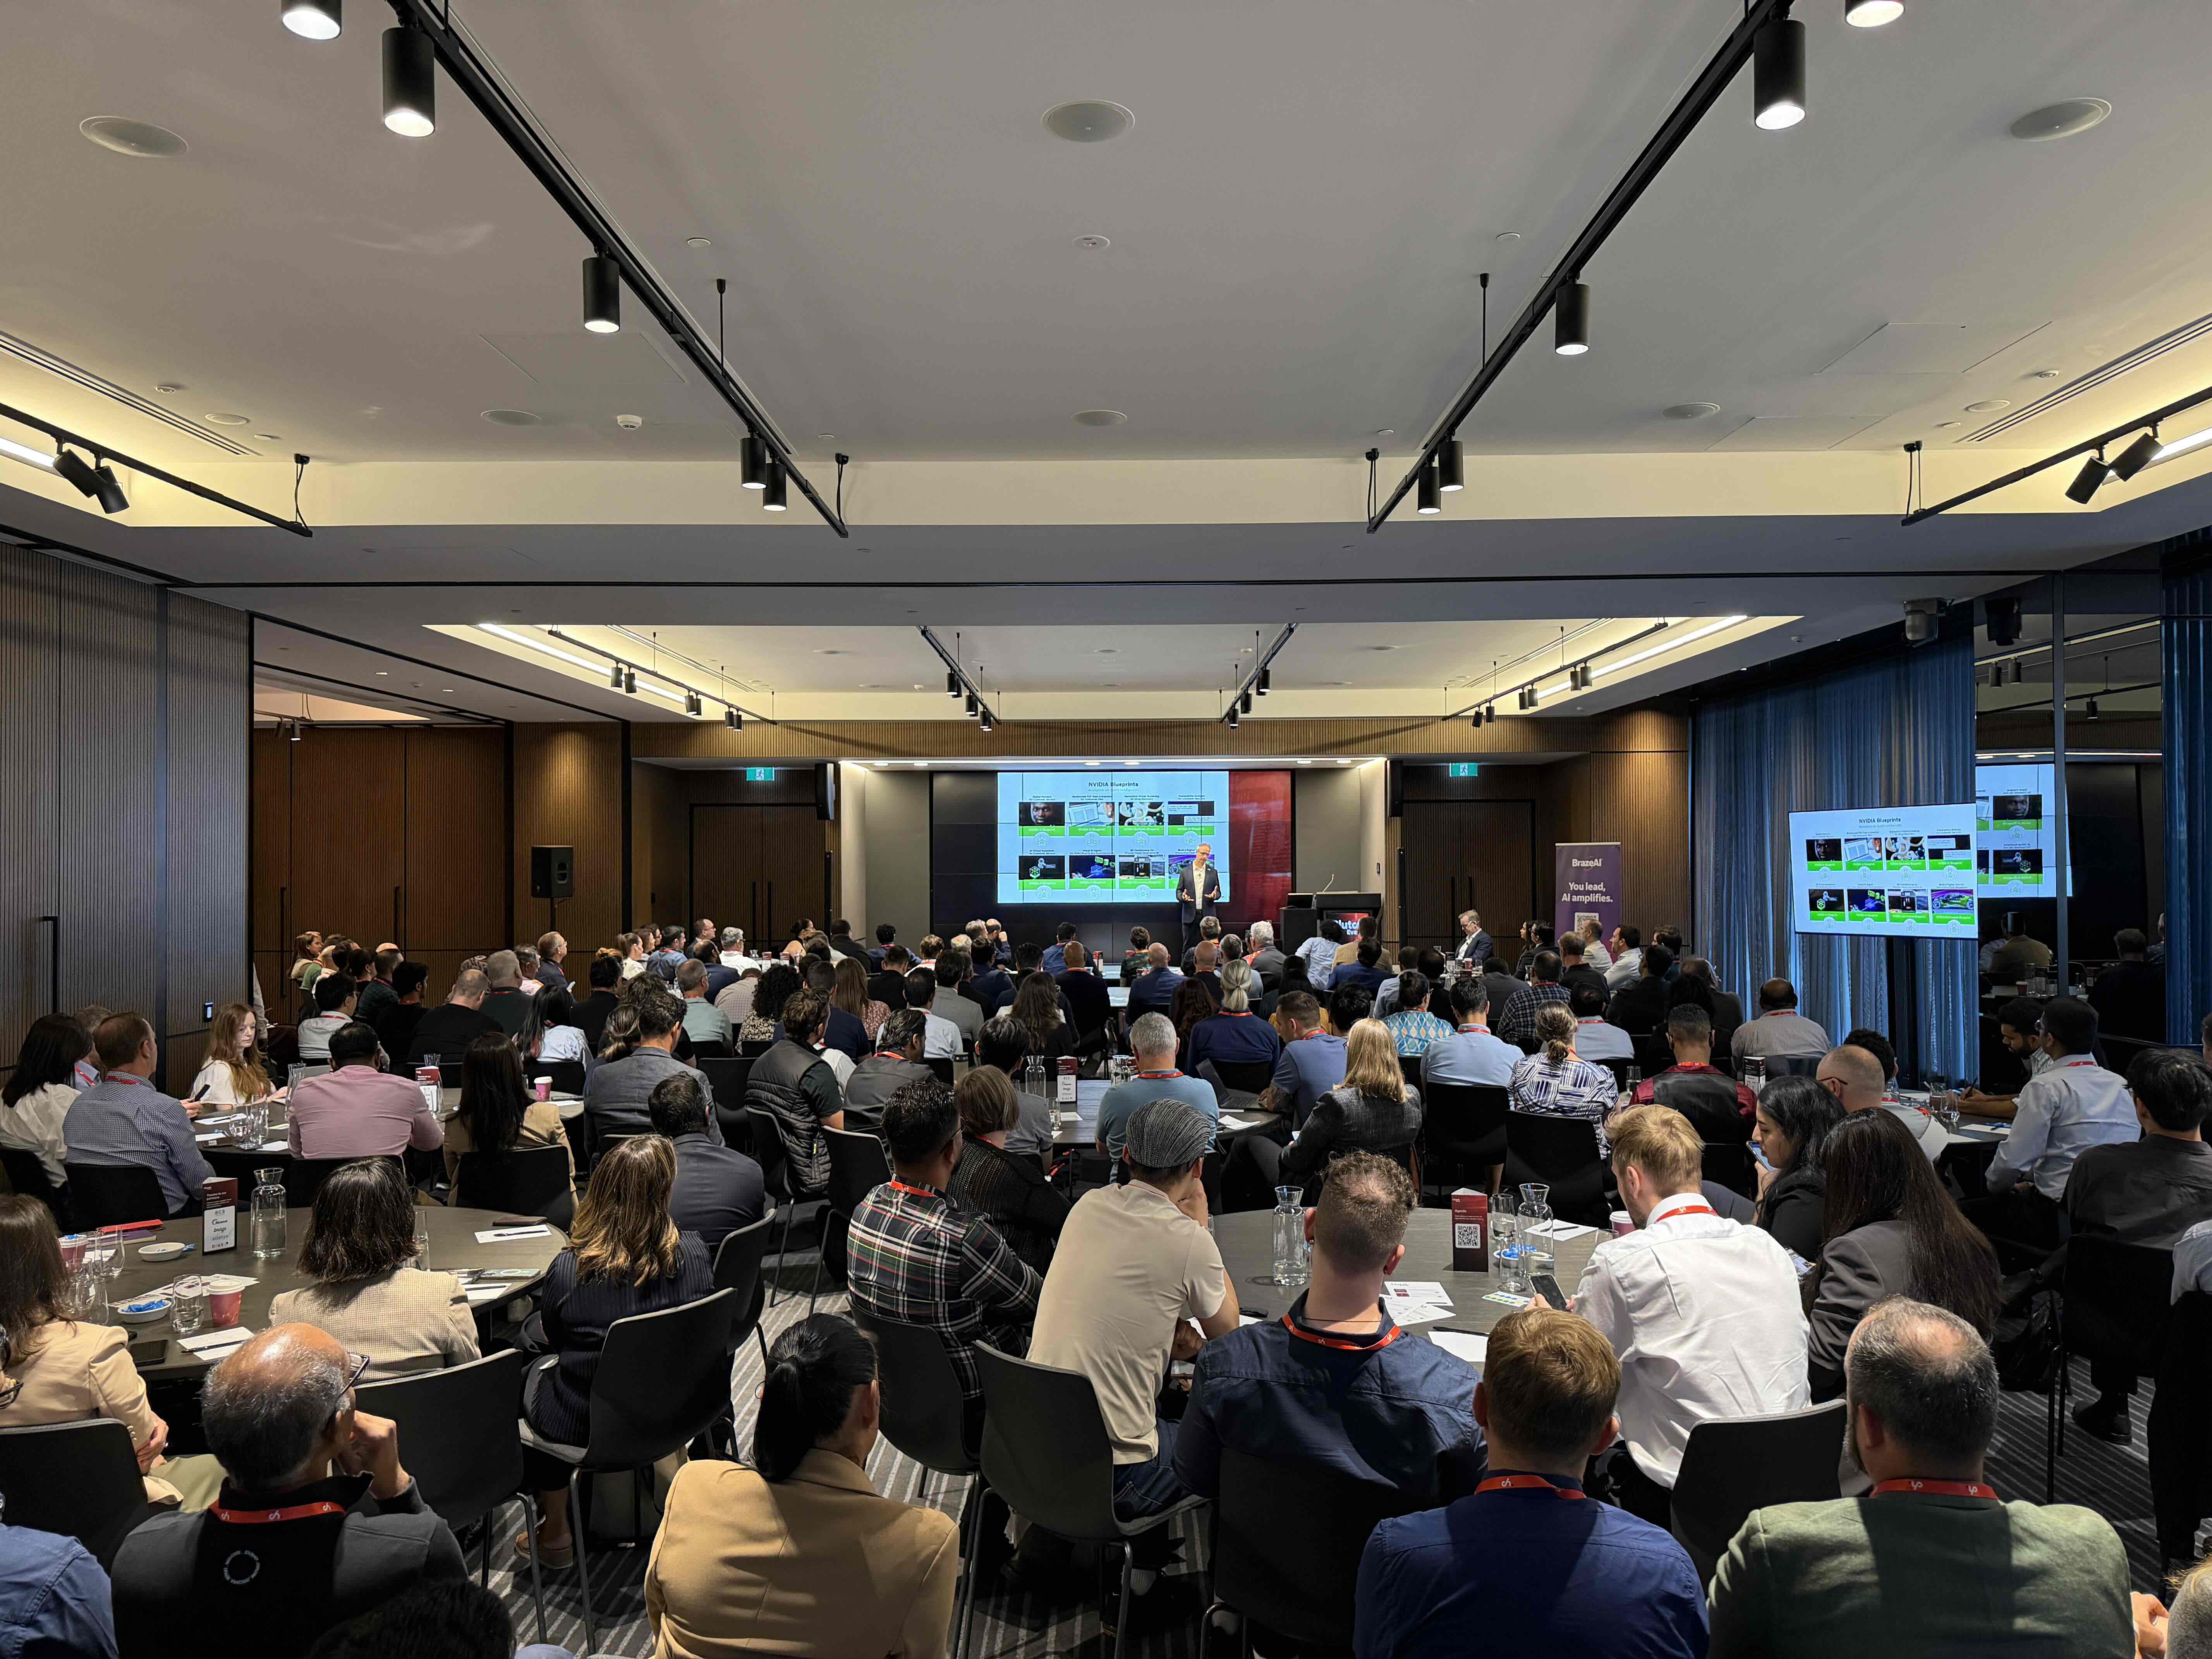
At most security conferences, application security is a stream inside a much broader event, never the room itself.
AppSec World is that room: the executives, programme owners and engineers who own how enterprise software gets built and shipped, comparing notes with their peers.
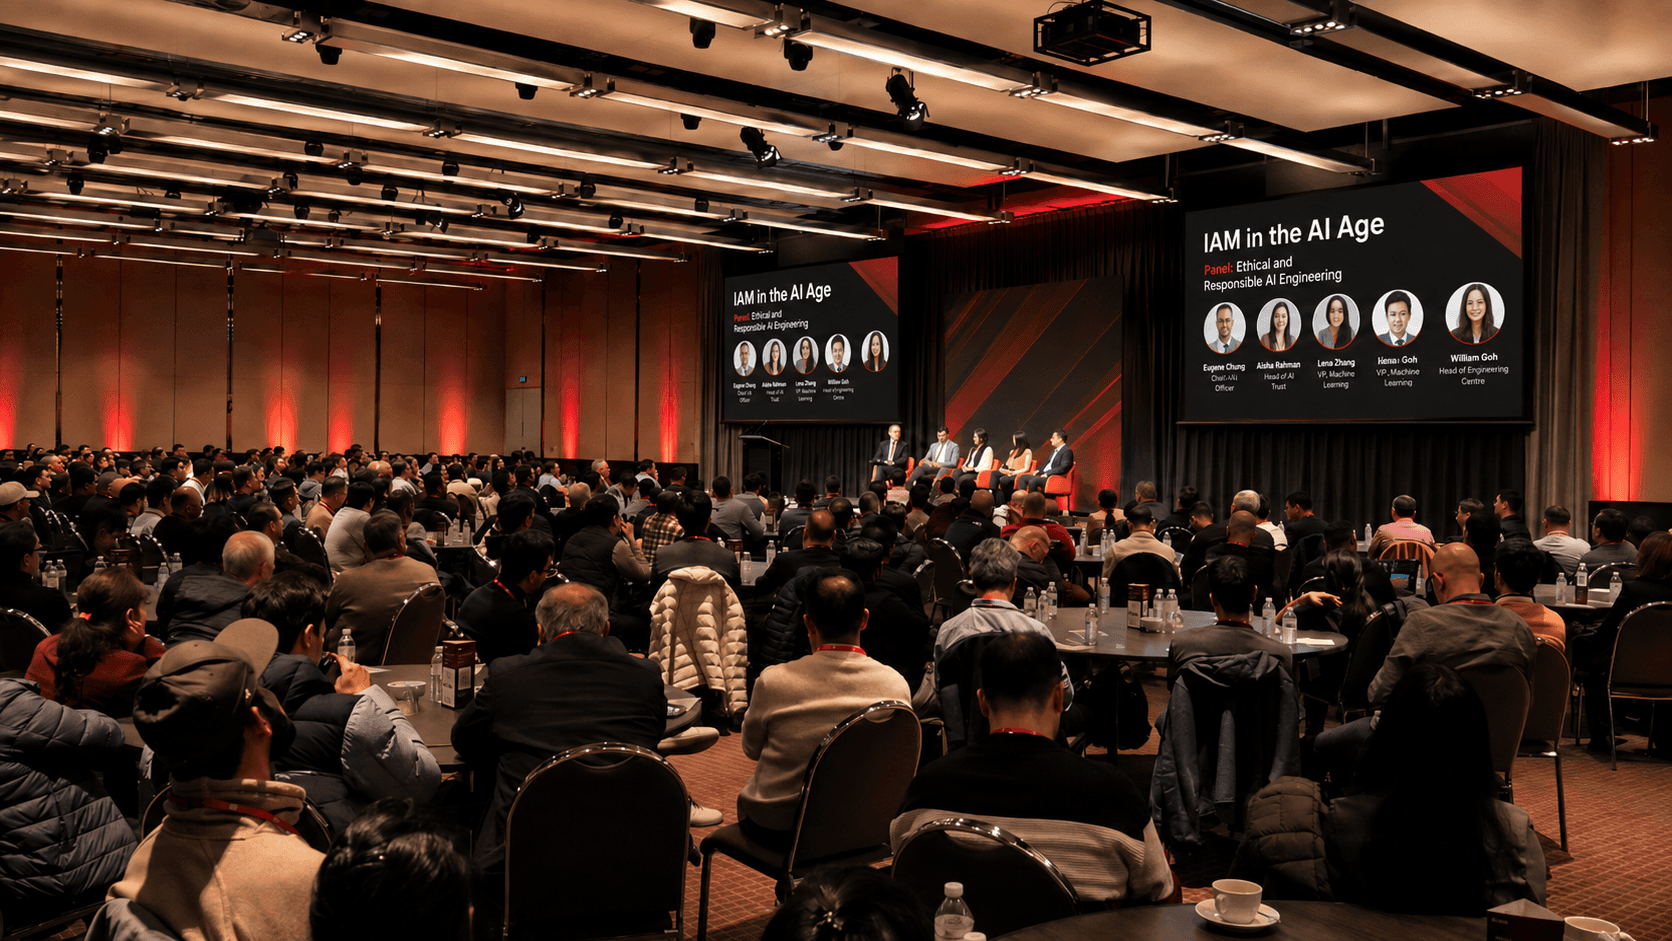
CISOs, CTOs and VPs of Security and Engineering who set the strategy and approve investment.
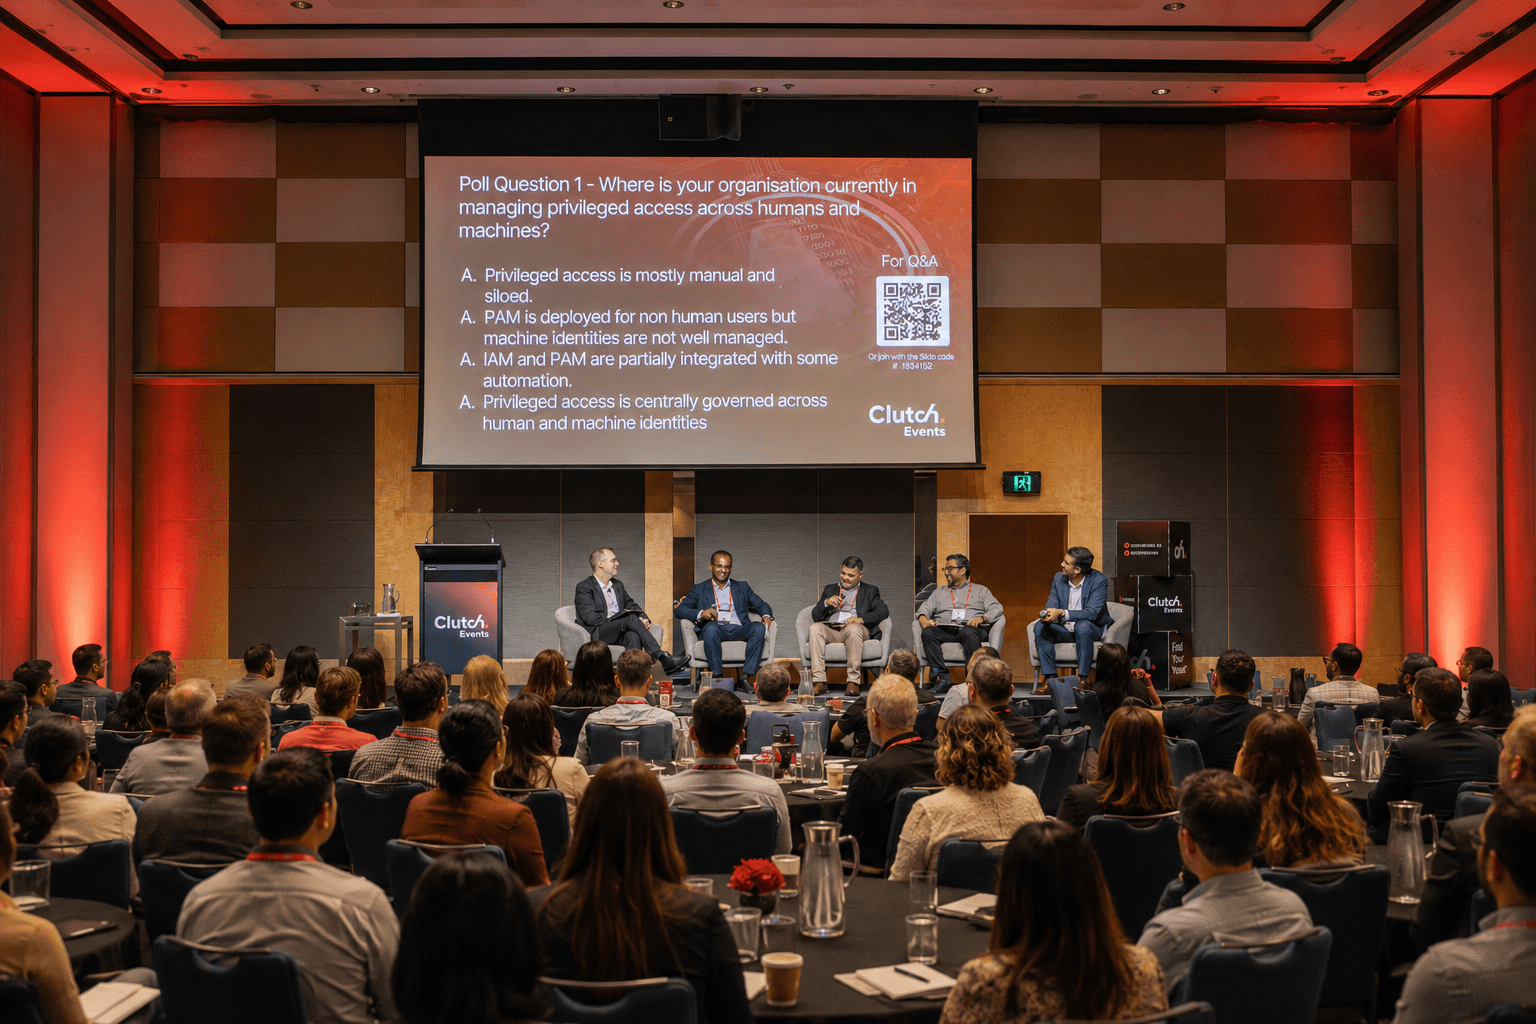
Heads, directors and managers of AppSec, Product Security and DevSecOps who own the roadmap and evaluate platforms.
The AppSec, product security, DevSecOps, platform and software engineers who build and operate the controls every day.
At least 85% of the audience are engineers, architects and security practitioners: the people writing the code, running the programme and dealing with the same problems you are.

 East CoastThu 9 Sep 2027 · New York Marriott MarquisExplore
 West CoastThu 20 May 2027 · Hilton San Francisco Union SquareExplore
 MelbourneThu 3 Jun 2027 · Event Centre on CollinsExplore
 SydneyThu 10 Jun 2027 · Doltone House Hyde ParkExplore
 LondonWed 27 Oct 2027 · Hilton London MetropoleExplore


Meet the engineers, architects and security leaders deciding how enterprise software gets secured — and which platforms get selected — at the world's most influential organisations.
At least 85% of the audience are engineers, architects and security practitioners — the people writing the code, running the programme and dealing with the same problems you are.
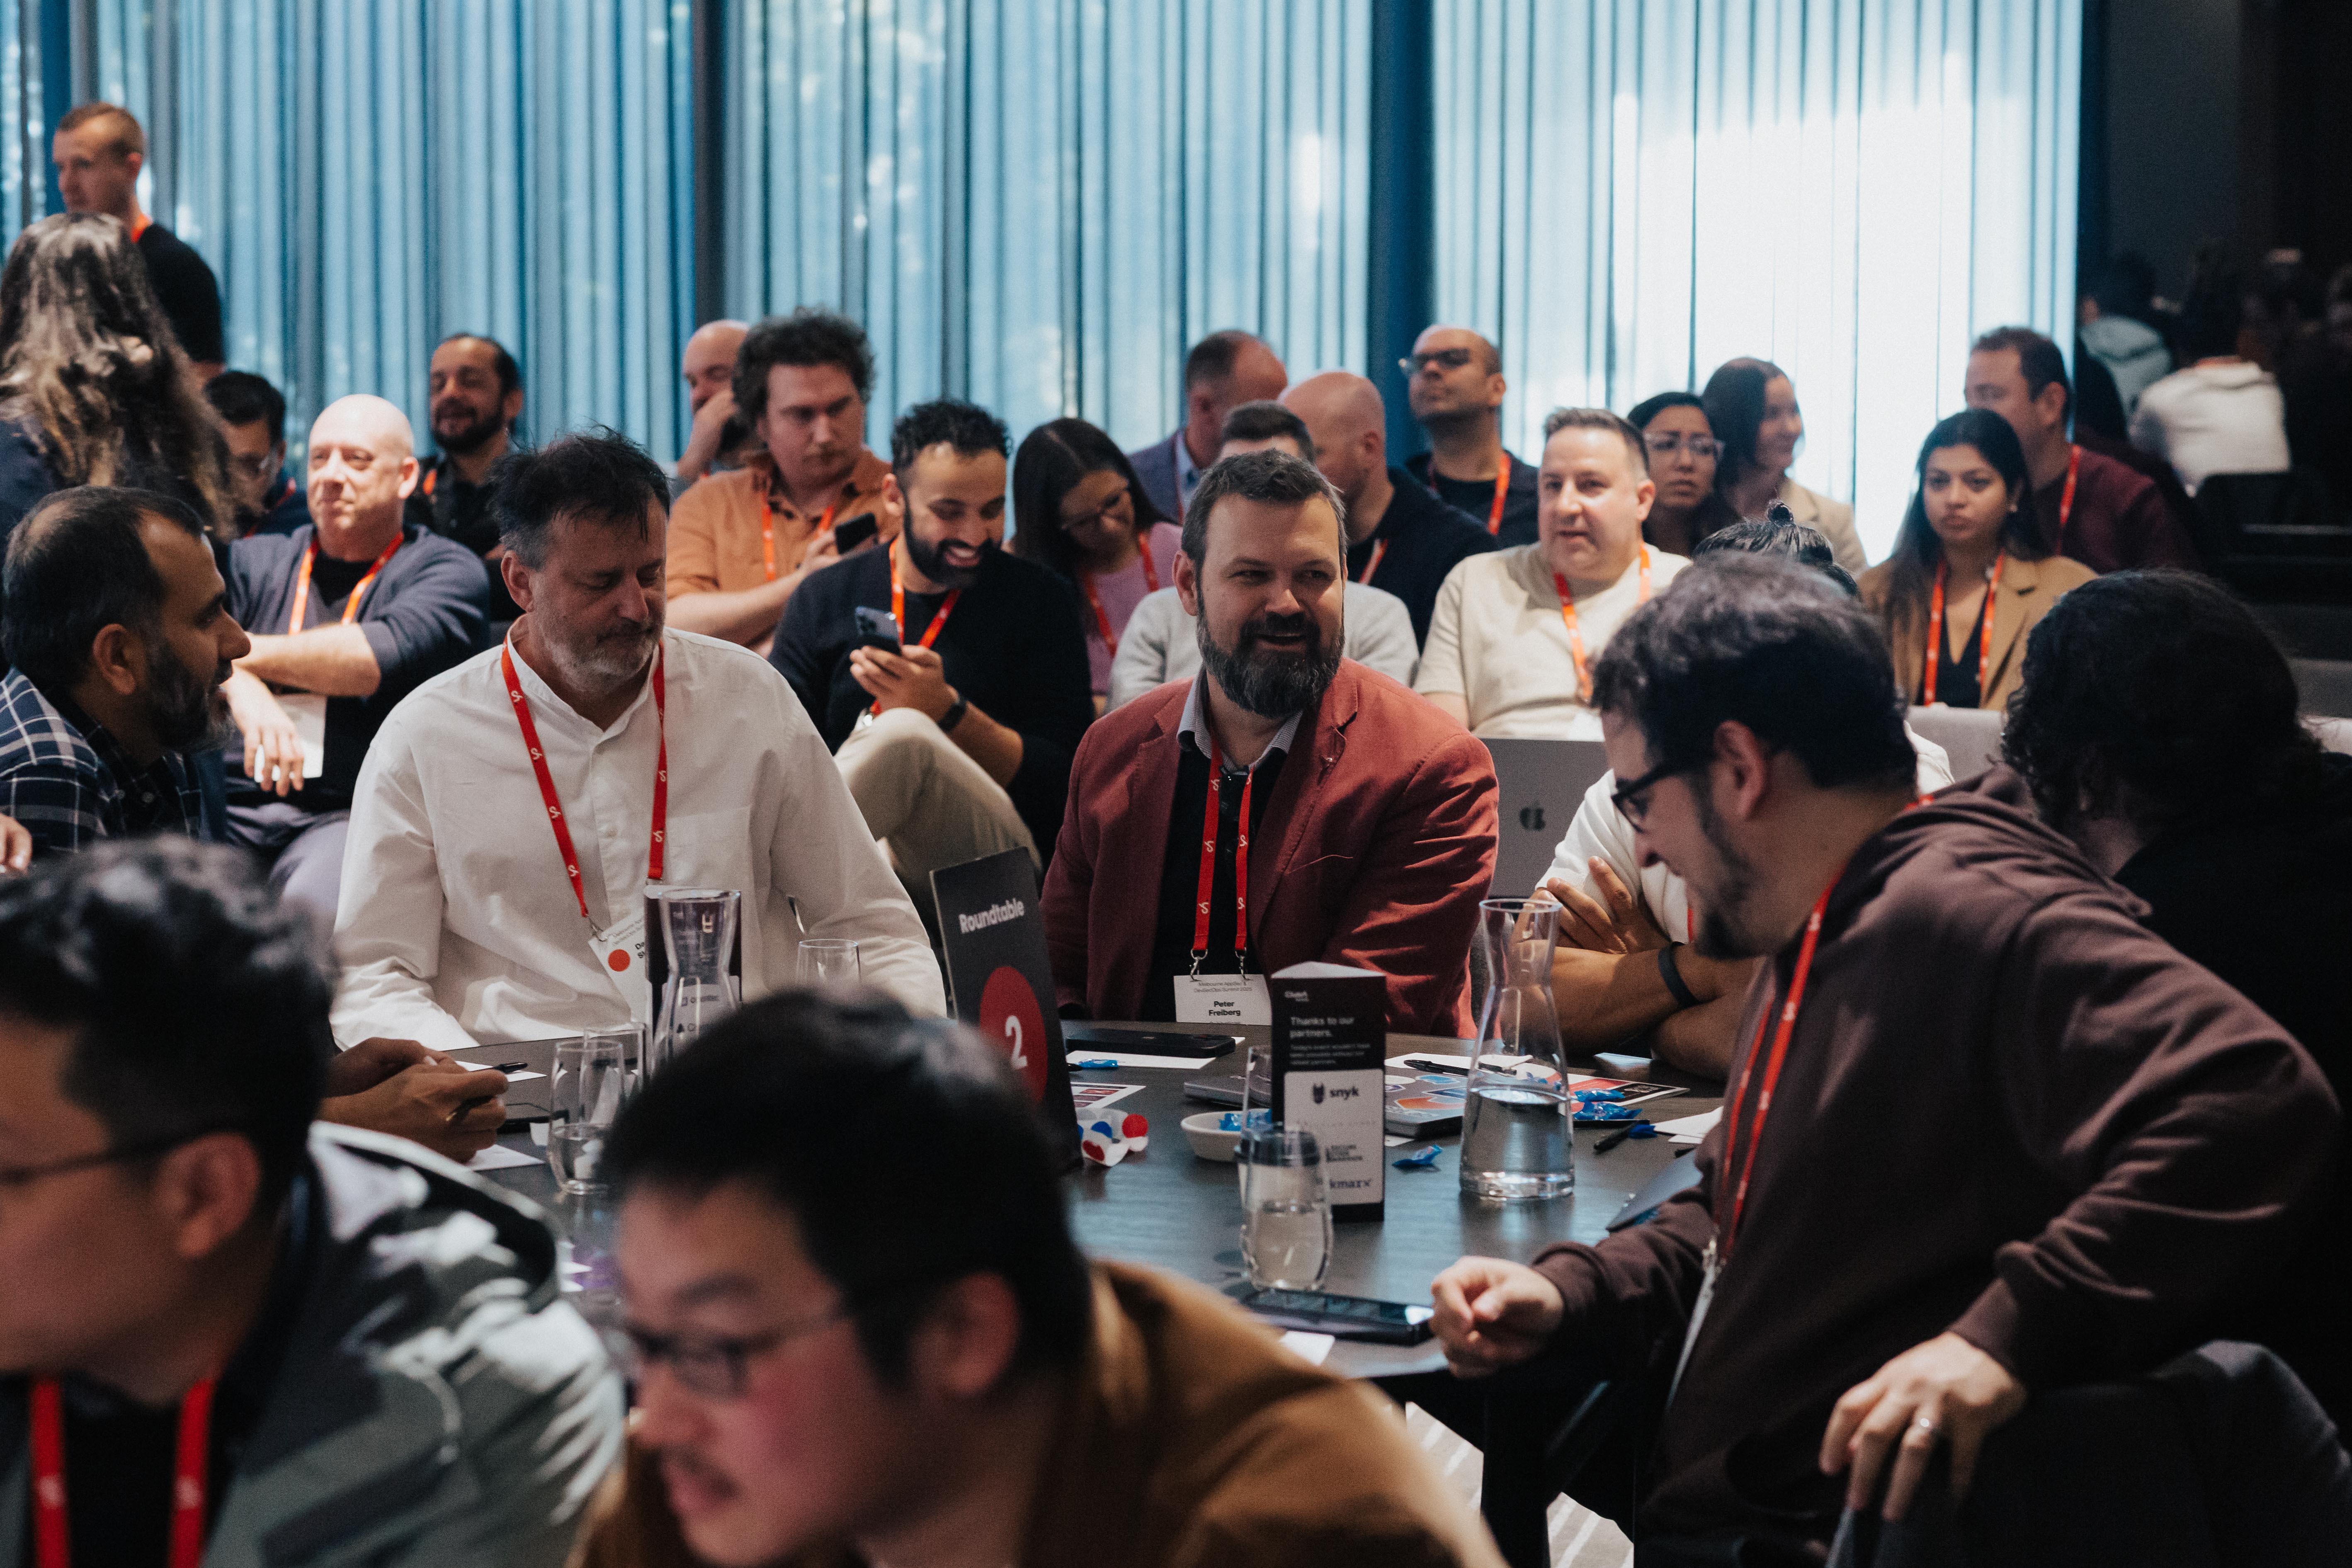
Every keynote, panel and case study is delivered by someone who has actually done the work. No product pitches from the stage and no theory — just what worked, what didn't and what it cost.
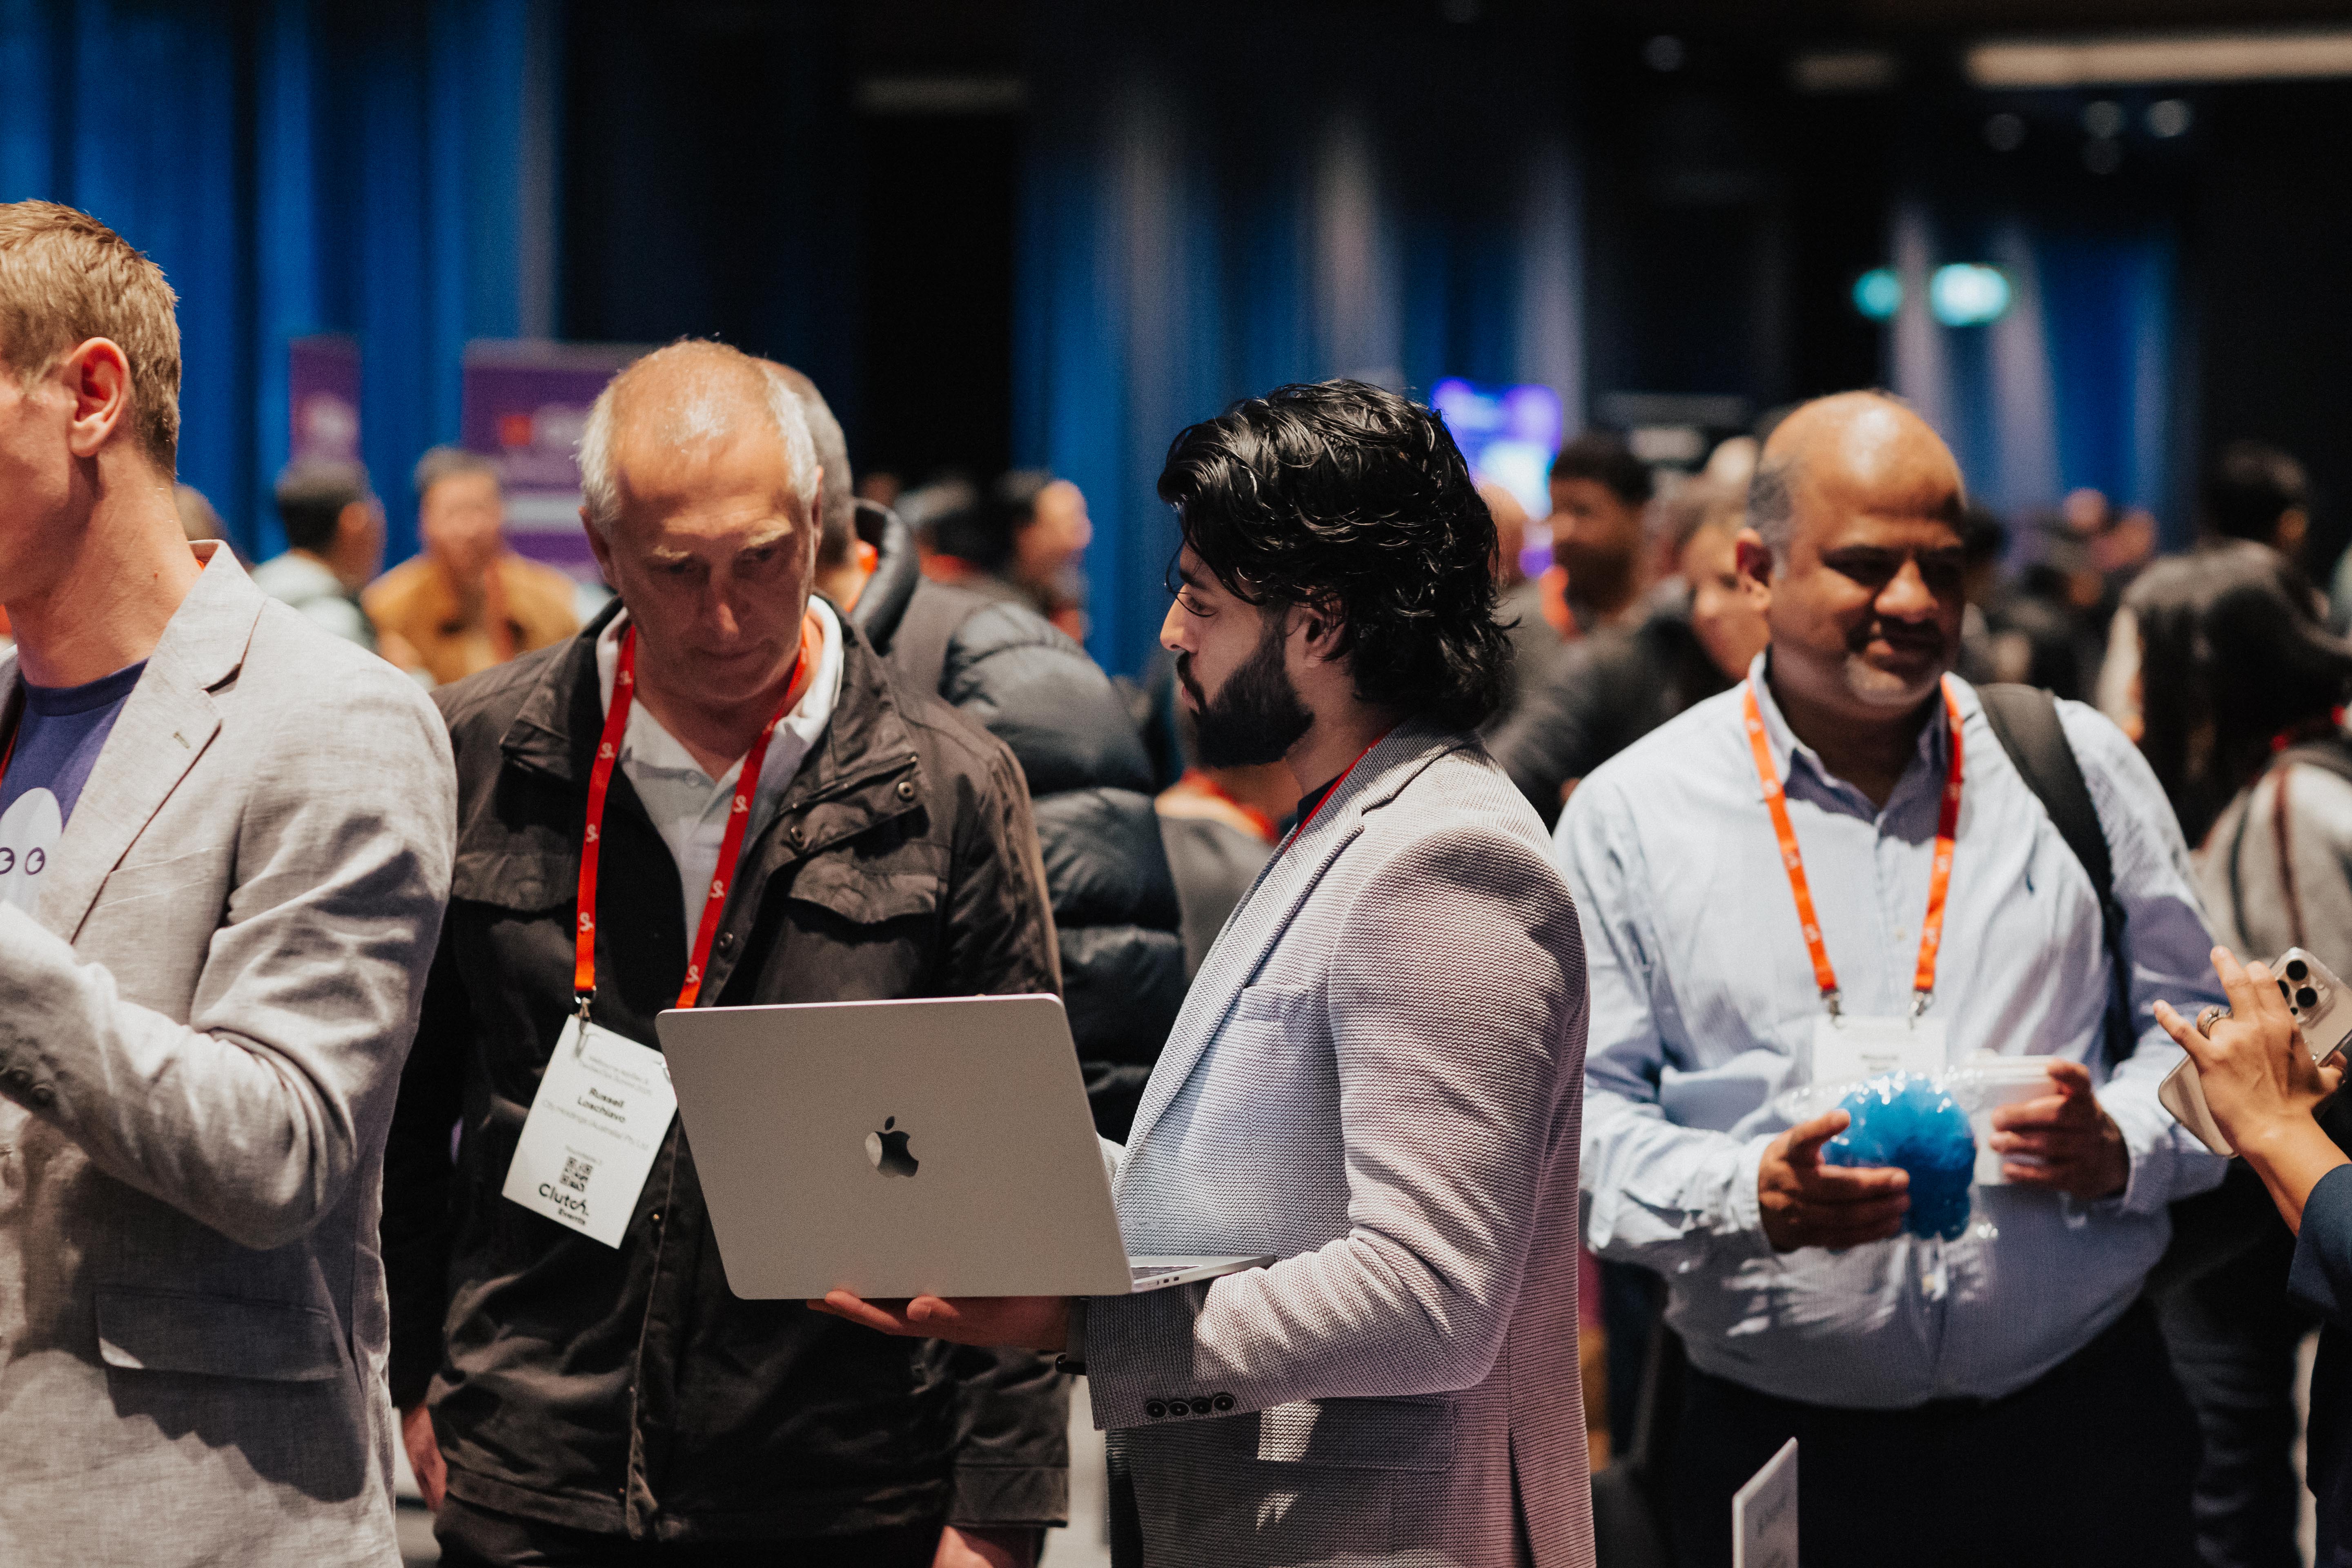
AppSec World connects the same challenges, ideas and lessons across five global markets — then brings them back to what matters in your region, your regulatory environment and your team.
Vulnerability prioritization that engineers trust: how to combine CVSS, EPSS, CISA KEV and reachability into fix-first rules and defensible SLAs.
Software supply chain security in practice: what an SBOM must contain, SBOM vs SCA, VEX, SLSA and the controls that stop the attacks that keep recurring.
AI code security for enterprises: the real risks of vibe coding, coding agents and slopsquatting, and the controls that govern AI-generated code at scale.